Where it applies
Use Nafath where it applies in Saudi Arabia, and other national sign-on services only after separate validation.
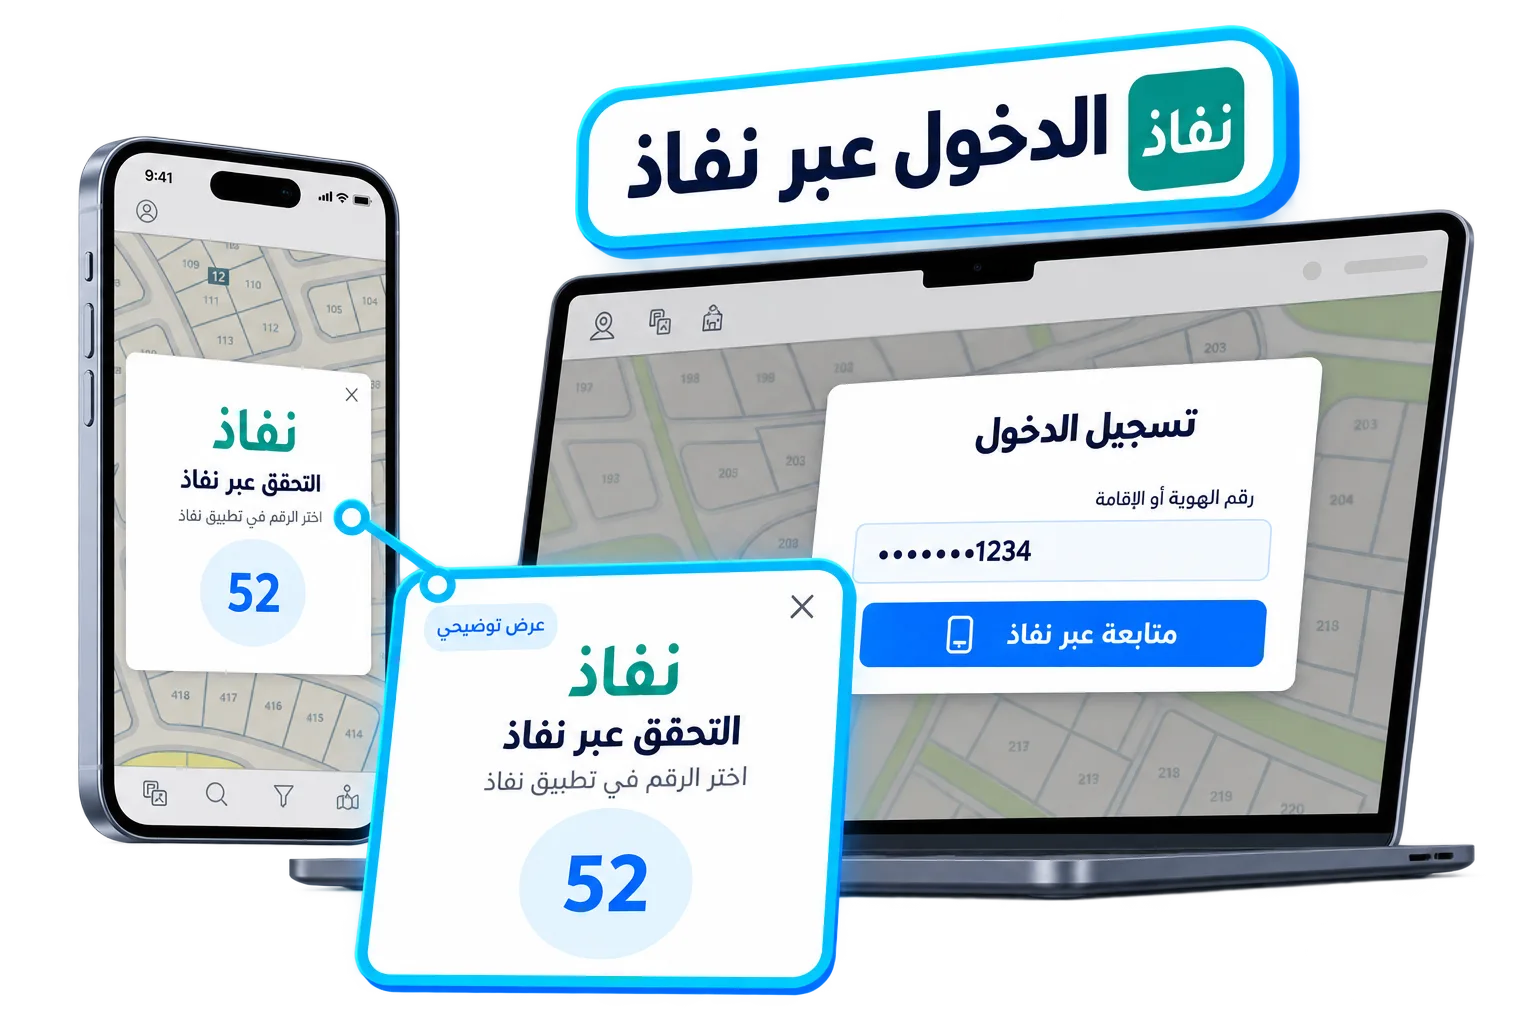
Plan digital access around the identity service each market supports. Connect an approved sign-on journey to tenant access rules, with verification and permissions kept distinct.
Where it applies
Use Nafath where it applies in Saudi Arabia, and other national sign-on services only after separate validation.
Not every record
A verified identity does not automatically grant access to every tenant record.
Only related work
Plan a trusted entry point without opening unrelated workspaces or records.
Where it applies
Use Nafath where it applies in Saudi Arabia, and other national sign-on services only after separate validation.
Not every record
A verified identity does not automatically grant access to every tenant record.
Only related work
Plan a trusted entry point without opening unrelated workspaces or records.
An identity service can help establish who is signing in. The tenant still decides what that person may see or do.
Connected view
Cut repeated identity steps where the approved provider supports them.
Right context
Apply tenant permissions after authentication, limited to authorized work.
Workflow data
Use a defined fallback when the identity service is unavailable.
Bring an approved Saudi identity step into eligible digital journeys. Connect the verification status to the next action the customer is allowed to take.
Move documents toward completion with less administrative friction. Connect approved versions, signers, and completion status to the transaction they belong to.
Make the payment step easier to understand and follow. Connect an approved payment journey to the invoice or reservation it supports, so requested, pending, and completed payments stay distinct.
Make your next development a connected journey